Závěrečná práce: Zargham Ahmad: Emulation and Detection of Cyber Threat Scenarios
Diplomová práce
Emulation and Detection of Cyber Threat Scenarios
Abstract
This diploma thesis focuses on automating adversary cyber threat scenarios utilizing the MITRE CALDERA tool, which is organized according to the kill chain model using the MITRE ATT&CK framework. The thesis aimed to facilitate the capture of data by Security Information and Event Management (SIEM) systems, specifically Wazuh SIEM, to enable a robust evaluation of threat modelling techniques. The thesis …více
Zadání práce
The goal of this diploma thesis is to prepare automated adversary cyber threat scenarios in MITRE CALDERA [1] organized according to the kill chain model using MITRE ATT&CK [2]. These scenarios should provide data that will be captured by Security Information and Event Management (SIEM) to allow evaluating threat modeling approaches. The work consists of the following subtasks:
- Familiarize with Advanced Persistent Threats and their techniques, MITRE ATT&CK, MITRE CALDERA tool for emulation of adversary scenarios, and Wazuh SIEM [3]. Familiarize also with the current state of cybersecurity emulation.
- Prepare evaluation environment and automated scenarios using cyber sandbox creator [4], vagrant, ansible, Wazuh SIEM, and MITRE CALDERA. It is possible to use also other tools.
- Prepare detection rules for all techniques from these scenarios that cannot be automatically detected by Wazuh. Use log events for this purpose. All techniques from scenarios must be detected, and SIEM must contain the necessary captured data.
- Configure human plugin from MITRE CALDERA so that benign human actions could be executed at the same time as adversary scenarios.
The scenarios should contain enough techniques from MITRE ATT&CK and the lateral movement tactic. Ideally, the scenarios must contain techniques from different MITRE ATT&CK tactics of the Enterprise matrix. The count of steps in scenarios should be realistic and the scenarios should not be artificially long. As a result, the diploma thesis should provide at least two different scenarios.
- [1] https://caldera.mitre.org/
- [2] https://attack.mitre.org/
- [3] https://wazuh.com/
- [4] https://gitlab.ics.muni.cz/muni-kypo-csc/cyber-sandbox-creator
21. 5. 2024 14:54, RNDr. Lukáš Sadlek, Ph.D., učo 445581
Přílohy
 angličtina
Práce na příbuzné téma
Seznam prací, které mají shodná klíčová slova.
-
Automatizovaná emulace scénářů kyberhrozeb
Bc. Denisa Půčková -
Coverage of cybersecurity threat detection in SOCaaS
Bc. Hanna Yarysh -
LLM-Based Analysis of Cybersecurity Blogs for Network Threat Detection
Bc. Michal Uherka -
Detekce pokročilých útoků v událostech Flowmon ADS
Ing. Petr Adamec -
Gathering Information from Community Threat Intelligence Platform
Šimon Bezek -
Application Log Analysis
Mgr. Júlia Murínová -
Automated Identification of Cyber Threat Scenarios
RNDr. Lukáš Sadlek, Ph.D., učo 445581 -
Attack graph generator in Python
Ing. Oldřich Machala
Složky
Soubory
-
Přidání souboru
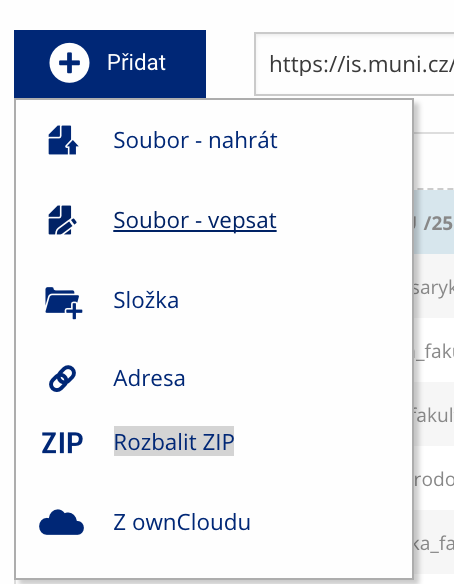 Soubor nebo složku lze nahrát pomocí tlačítka Přidat.
-
Další operace se soubory
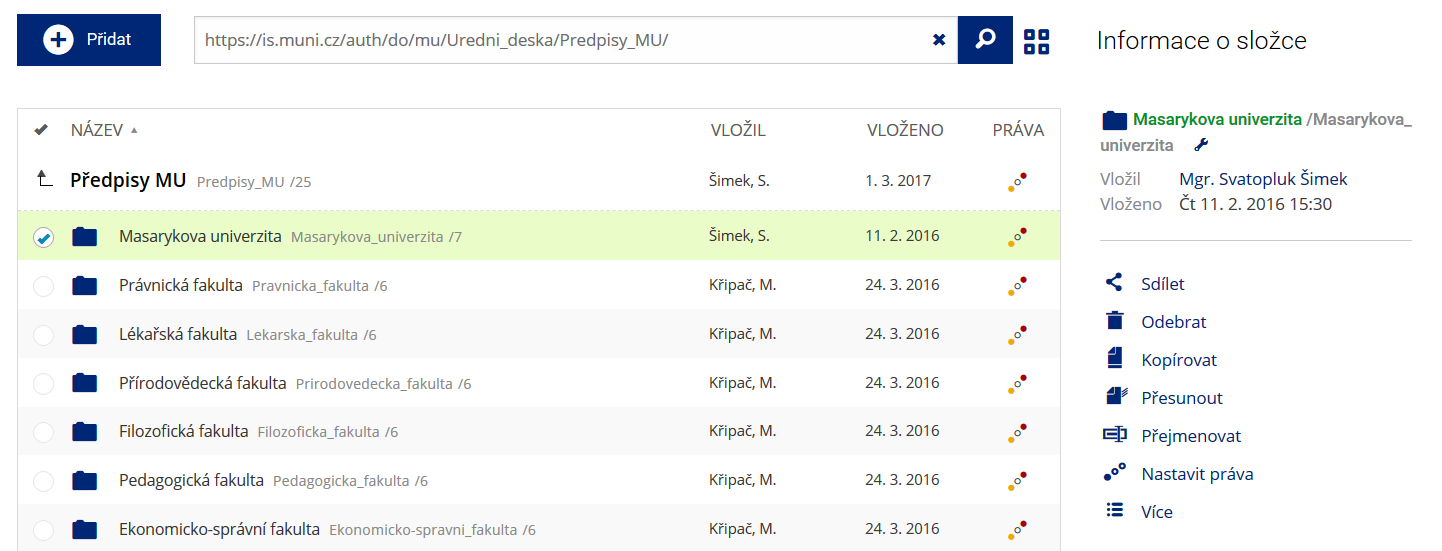 Podrobnosti lze zjistit označením příslušného řádku.
-
Pohled pro experty
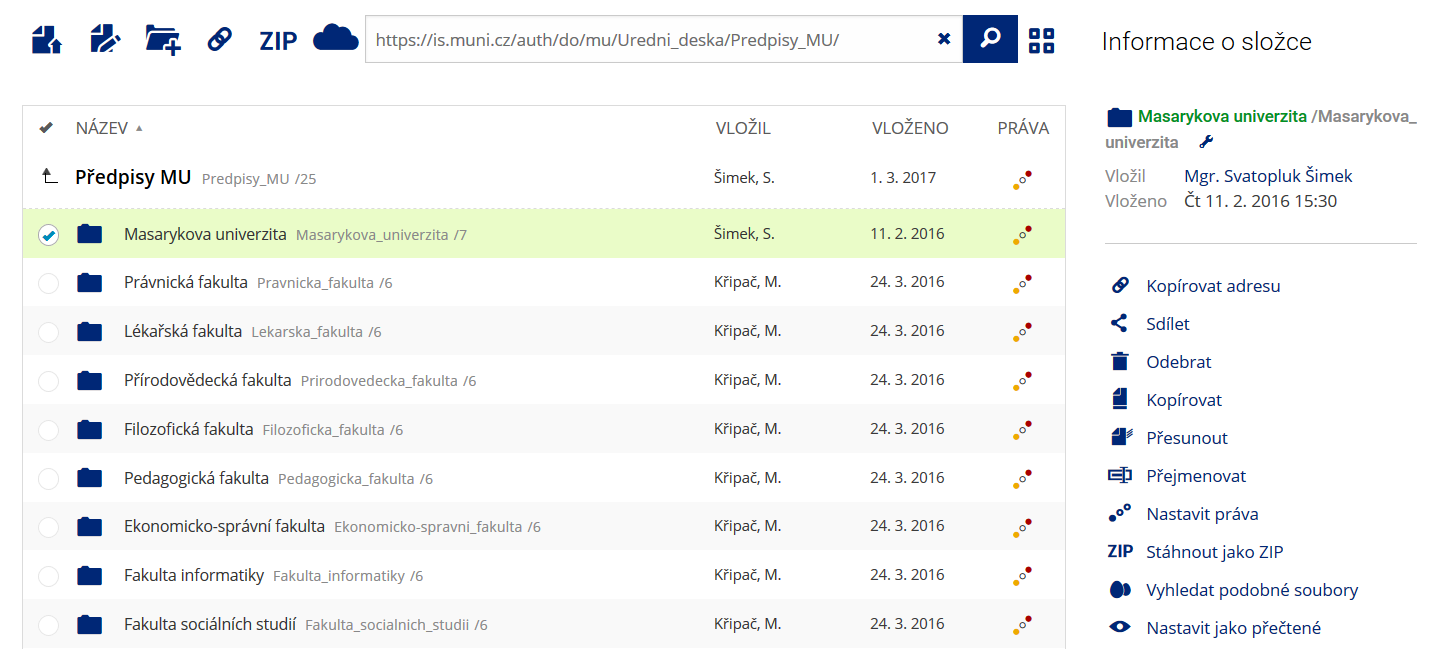 Pro častou práci je možné zvolit režim Více možností.
-
Vyhledávání souborů
 Vyhledávaný výraz můžete zadat přímo do adresního řádku.
-
Rychlý přístup k souborům
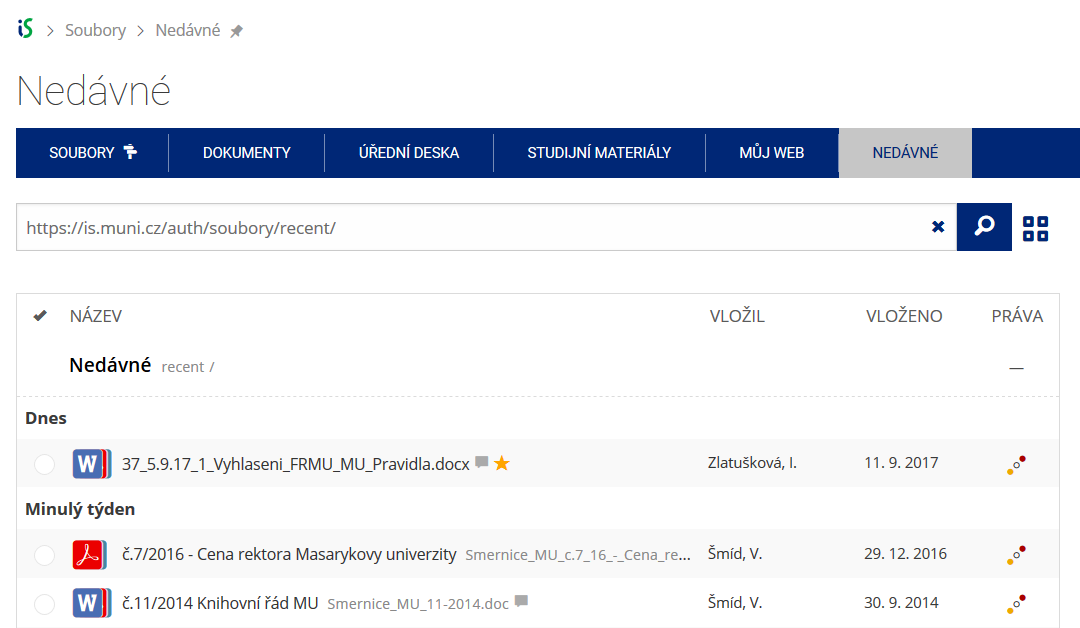 Pomocí funkce Nedávné je možné se rychle vrátit k právě prohlíženým souborům. Oblíbené soubory je také možné označit Hvězdičkou.