Závěrečná práce: Ondrej Kužlík: Detection of masquerading traitors from computer usage
Bakalářská práce
Detection of masquerading traitors from computer usage
Anotace
Cieľom tejto práce je použiť techniky procesnej ťažby na detekciu prítomnosti maskujúcich sa zradcov z denníku udalostí systému a určiť efektivitu tohto prístupu. Prvá časť práce čitateľovi predstavuje procesnú ťažbu a detekciu hrozieb, zatiaľ čo druhá časť sa sústredí na implementáciu prístupu a analýzu efektivity jeho výstupov postredníctvom predstavenia výsledkov dotazníku.
Abstract
This thesis aims to use process mining techniques to detect the presence of masquerading traitors from a system's event log and to determine the efficiency of this approach. The first part of the thesis describes process mining and threat detection to the reader, whereas the second part focuses on the implementation of the approach and analysis of the efficiency of its outputs by the means of a presenting the results of a questionnaire.
Zadání práce
The student will create his own dataset on which he will demonstrate the usability of his implementation. This dataset will be used for multiple visualizations (for example, for the computer usage of each working day in the week). Each visualization will include one injected attack, which might be caused by the masquerading traitor in the organization. Then, the student will evaluate the effectiveness of those visualizations on several participants.
25. 5. 2021 15:18, RNDr. Martin Macák, Ph.D., učo 410452
 angličtina
Práce na příbuzné téma
Seznam prací, které mají shodná klíčová slova.
-
Comparison of data-oriented and process-oriented approaches for insider attack detection from audit logs
Ing. Marek Laššák -
Vliv změny procesní definice na kvalitu výstupů procesního dolování
Bc. František Buhla -
The utilization of process mining for insider attack detection in information systems
Bc. Daniel Rozehnal -
Process Mining Software Evaluation
Ing. Tamara Babálová -
Process mining for contract review process optimization
Mgr. Magdaléna Lišková -
Rekonstrukce průchodů bezpečnostními cvičeními a jejich základní vizualizace
Mgr. Ondrej Svoreň -
Exploratory process mining analysis of video game achievements
Ing. Júlia Jamnická -
Interaktivní zobrazení procesních grafů
Ing. Tomáš Kadavý
Složky
Soubory
-
Přidání souboru
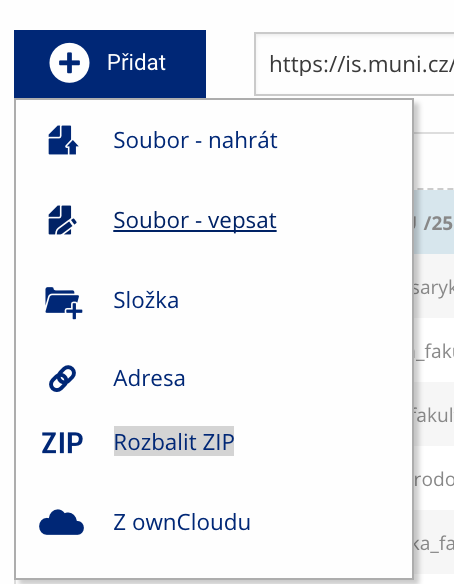 Soubor nebo složku lze nahrát pomocí tlačítka Přidat.
-
Další operace se soubory
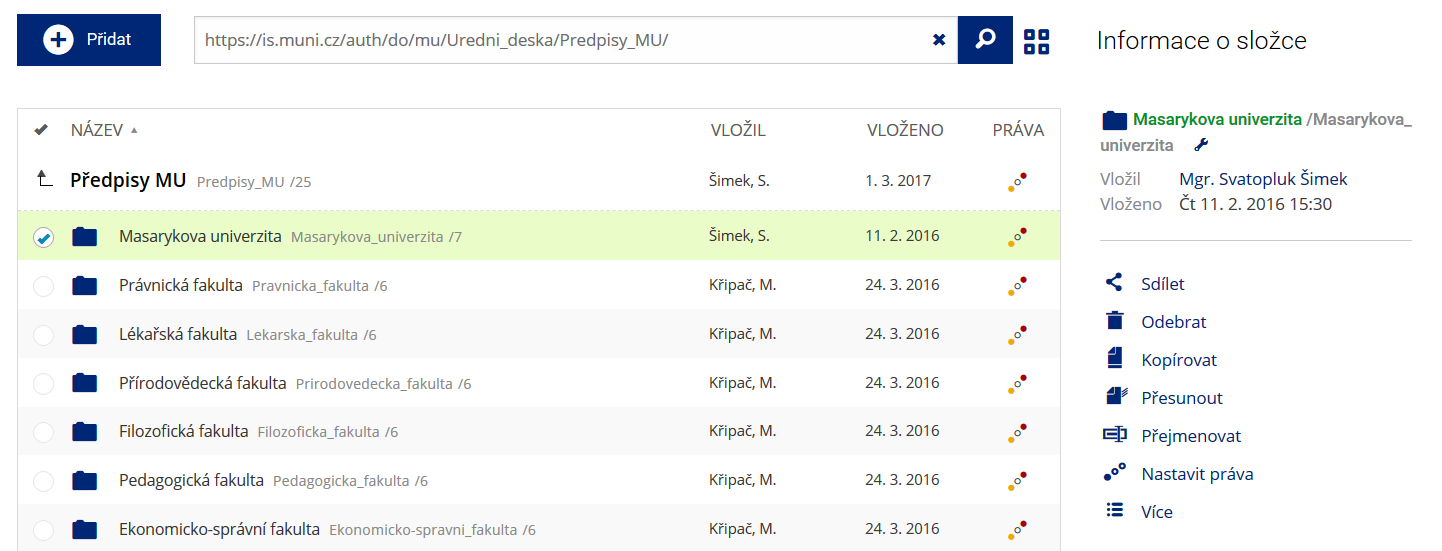 Podrobnosti lze zjistit označením příslušného řádku.
-
Pohled pro experty
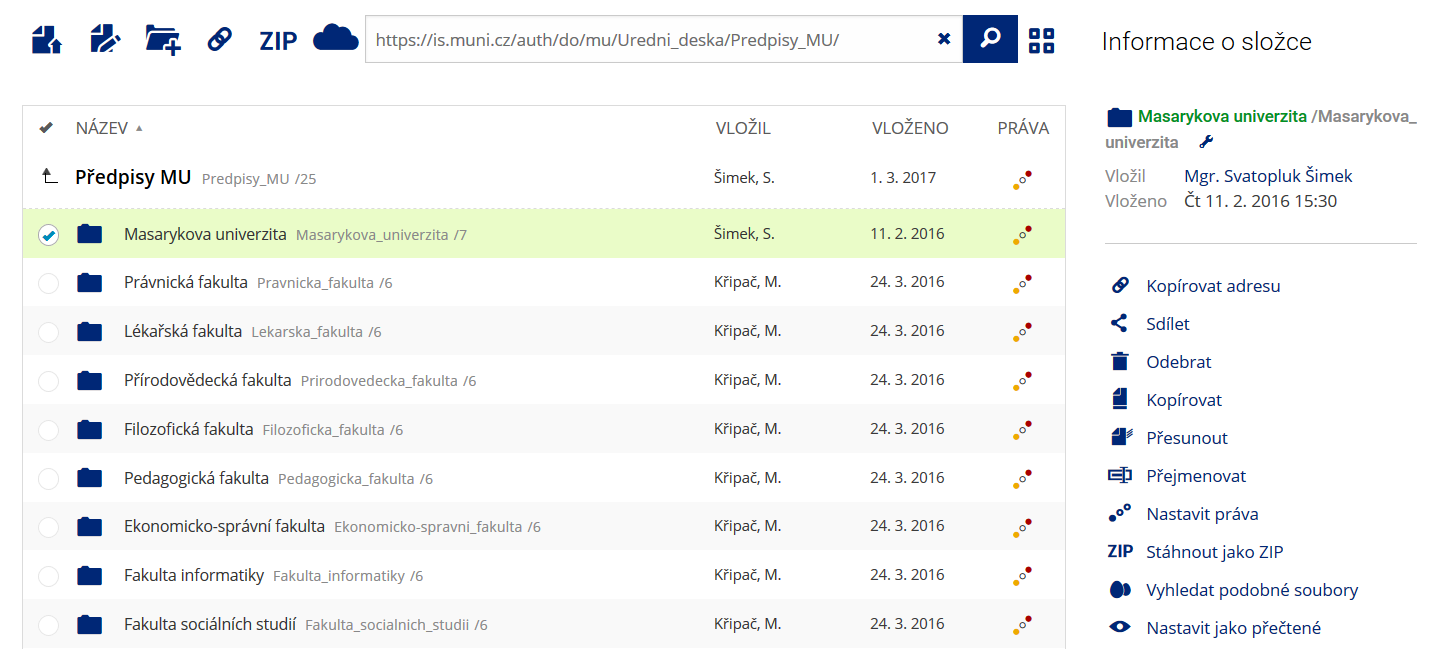 Pro častou práci je možné zvolit režim Více možností.
-
Vyhledávání souborů
 Vyhledávaný výraz můžete zadat přímo do adresního řádku.
-
Rychlý přístup k souborům
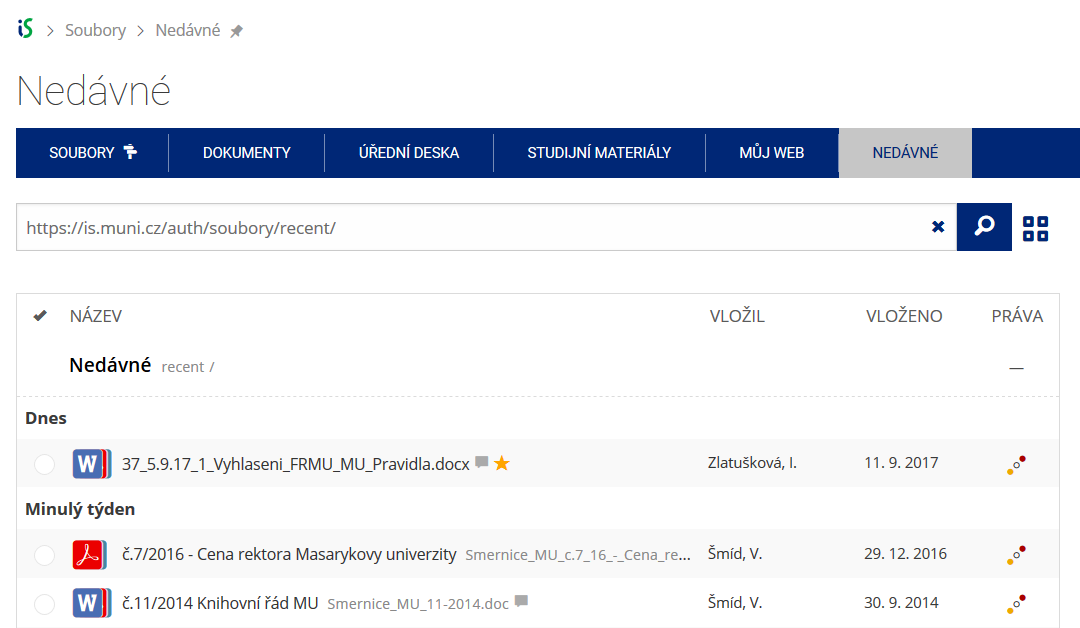 Pomocí funkce Nedávné je možné se rychle vrátit k právě prohlíženým souborům. Oblíbené soubory je také možné označit Hvězdičkou.