Závěrečná práce: Bc. Jiří Michalík: Measuring vulnerability patch delay in Android kernel
Diplomová práce
Measuring vulnerability patch delay in Android kernel
Anotace
Tato práce analyzuje zpoždění šíření záplat z Linuxu do jader Androidu. Implementujeme automatizovaný nástroj pro zjišťování správného šíření záplat do větví jádra Androidu. Na základě výstupů z automatizovaného nástroje poskytneme analýzu zaměřenou především na měření zpoždění šíření záplat a odhalování anomálií v šíření záplat. Dále vyvineme mechanismus pro identifikaci nejzranitelnějších částí jádra …více
Abstract
This thesis analyses patch propagation delay from Linux to Android kernels. We implement an automated tool to detect the correct patch propagation into Android kernel branches. Based on the outputs from the automated tool, we provide analysis primarily focused on measuring the patch propagation delay and detecting anomalies in the propagation of patches. Furthermore, we develop a mechanism to identify …více
Zadání práce
Context
The Android operating system is well-known for kernel fragmentation on endpoint devices. This fragmentation causes delays or even prevents kernel updates, leading to devices running outdated kernel versions. In 2019, Google launched the Generic Kernel Image (GKI) project to address this issue, aiming to reduce fragmentation and speed up kernel update distribution.
Research goal
The primary goal of this thesis is to measure the propagation delay of security patches in the Android kernel. The student will collect and analyze data on the propagation of Linux kernel patches to the Android kernel. This analysis will include a subset of historical CVEs introduced in the Android Security Bulletin and CVEs not yet presented in the bulletin. The focus will be on patch delay propagation in the context of the GKI project. The thesis will also explore weaponization potential of these CVEs, given an attacker having access to sufficient information prior to the publication of CVEs in Android Security Bulletin.
The practical part will:
- Develop a tool to automatically mine the propagation of Linux kernel updates to the Android kernel.
- Deliver data analysis of security-patch propagation from Linux kernel to Android kernel including results discussion.
- Study historical CVEs and CVEs not yet introduced in Android Security Bulletin, concentrating on their weaponization potential based on open-source information.
- Measure the empirical propagation delay distribution, assessing the time taken from the application of a security patch upstream to its implementation on end devices, utilizing existing research.
18. 12. 2024 09:15, RNDr. Adam Janovský, Ph.D., učo 410390
 angličtina
Práce na příbuzné téma
Seznam prací, které mají shodná klíčová slova.
-
Secure software development process and tools for Android applications
Mgr. Peter Franek -
Mobile application secure phone
Bc. Jakub Uličný -
Modern obfuscation techniques
Mgr. Roman Oravec -
The Security of Flutter`s Architecture
Mgr. Maroš Zelenák -
Analýza a rozšíření ochranných mechanismů knihovny Talsec Security
Mgr. Tomáš Soukal -
Bezpečnostní aspekty distribuce aplikací pro OS Android
Mgr. Radim Lipovčan, učo 433279 -
Steganografie a stegoanalýza
RNDr. Roman Žilka -
Key distribution and authentication protocols for wireless sensor networks
doc. RNDr. Petr Švenda, Ph.D., učo 4085
Složky
Soubory
-
Přidání souboru
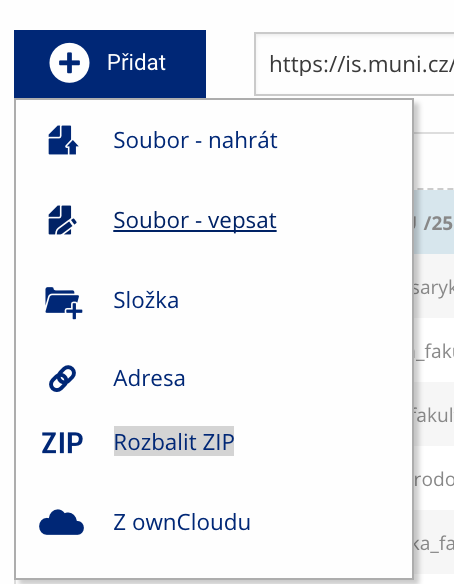 Soubor nebo složku lze nahrát pomocí tlačítka Přidat.
-
Další operace se soubory
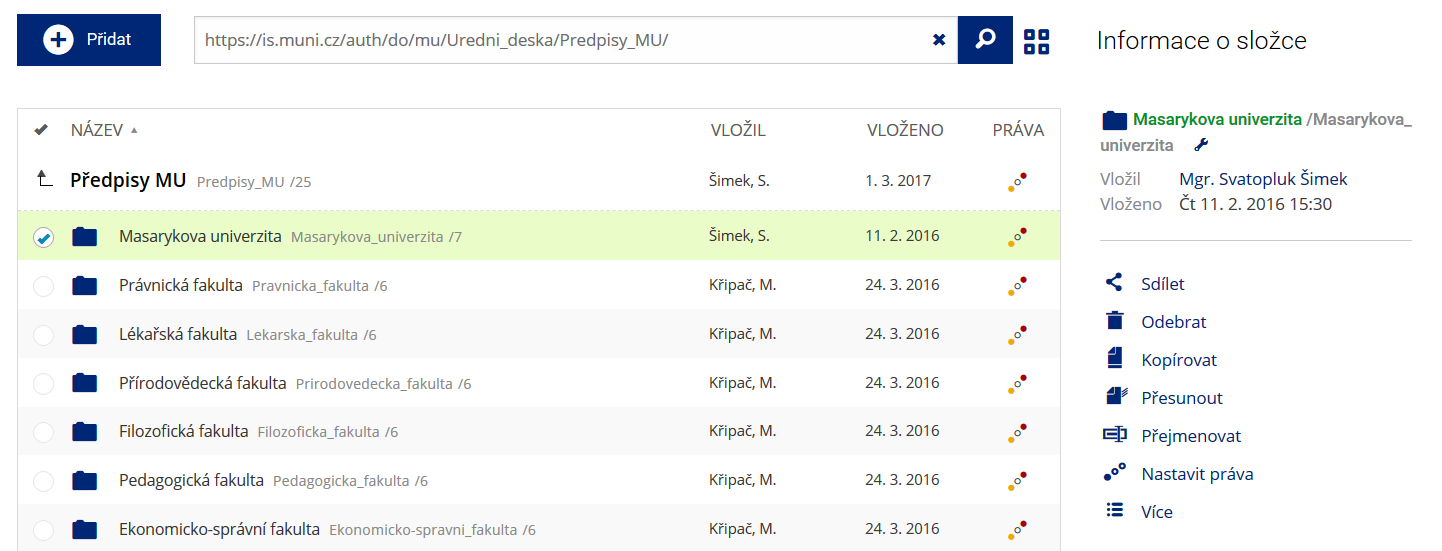 Podrobnosti lze zjistit označením příslušného řádku.
-
Pohled pro experty
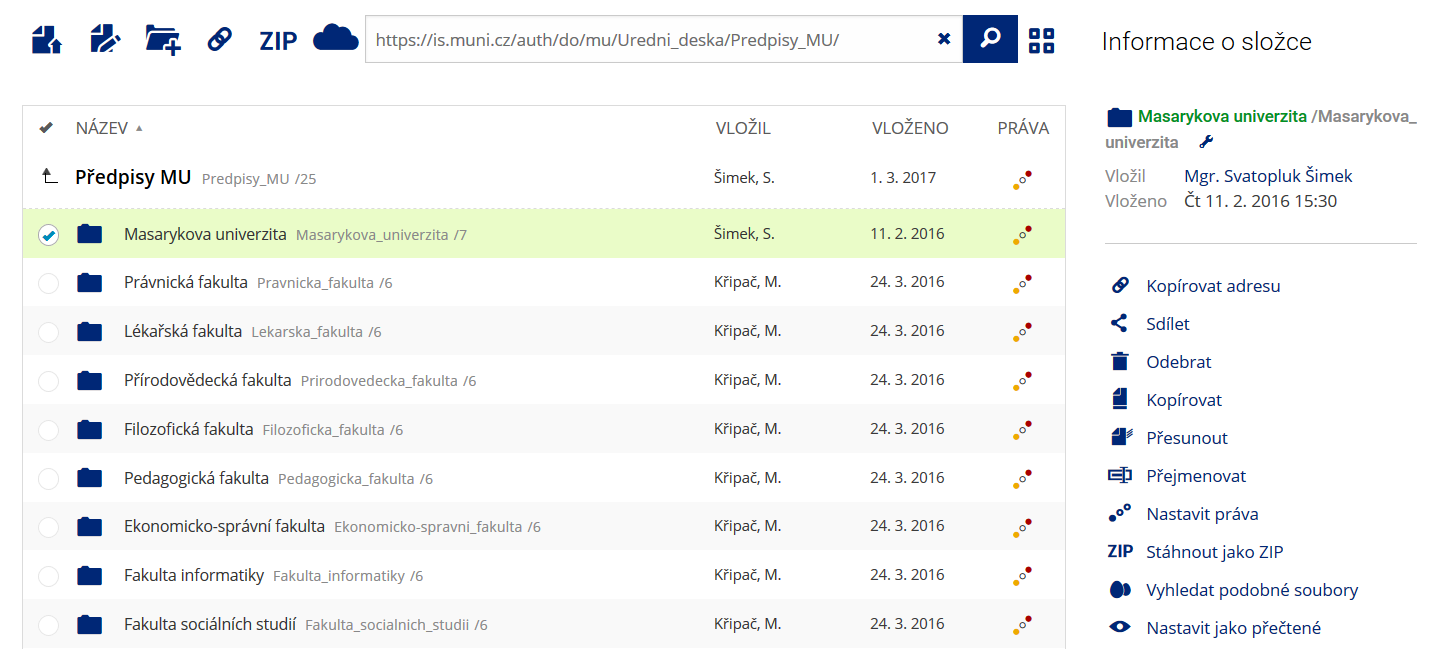 Pro častou práci je možné zvolit režim Více možností.
-
Vyhledávání souborů
 Vyhledávaný výraz můžete zadat přímo do adresního řádku.
-
Rychlý přístup k souborům
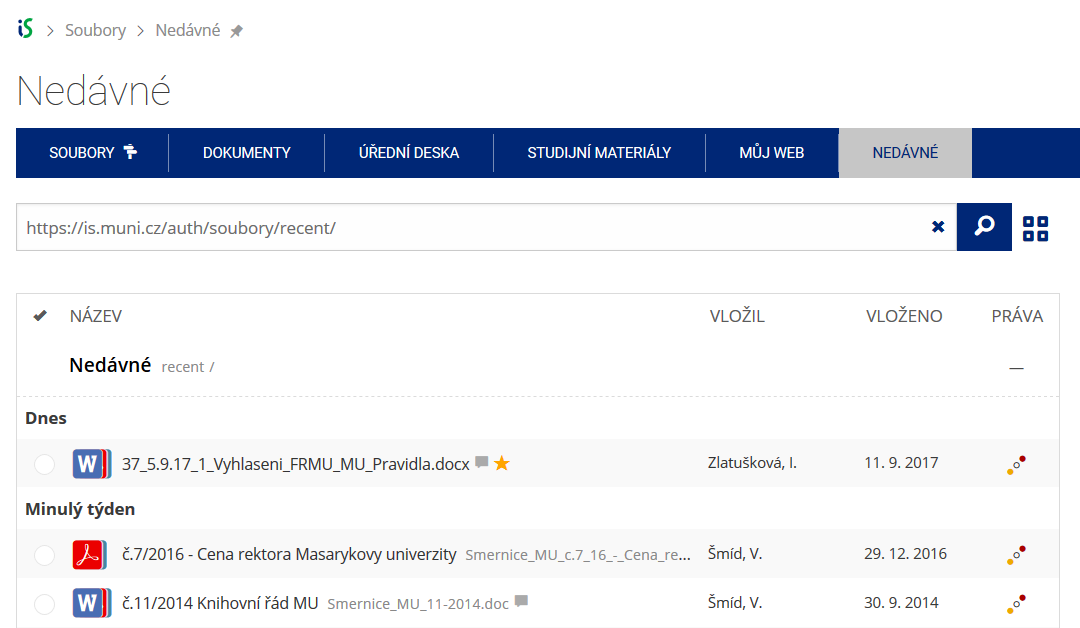 Pomocí funkce Nedávné je možné se rychle vrátit k právě prohlíženým souborům. Oblíbené soubory je také možné označit Hvězdičkou.