Závěrečná práce: Bc. Peter Benčík: APDUFuzzer: blackbox recovery of smartcard API
Diplomová práce
APDUFuzzer: blackbox recovery of smartcard API
Anotace
Špecifikácia aplikačného programového rozhrania čipových kariet často nie je pre nezávislých výskumníkov k dispozícii. Tí sa potom musia spoliehať na vlastné bádanie v oblasti reverzného inžinierstva. Táto práca sa zaoberá možnosťou použitia inštrumentovaného fuzzing testovania na zjednodušenie tohto procesu. Demonštrujeme uskutočniteľnosť tohto návrhu jednoduchou implementáciou používajúcou nástroj …více
Abstract
Specification of API for smart card applets is often not available for independent researches, who must, therefore, rely on their own reverse engineering efforts. In this work, we explore the possibility to use guided fuzzing combined with power consumption analysis to make this task more efficient. We provide a proof-of-concept implementation of this idea using AFL fuzzer and PicoScope digital oscilloscope …více
Zadání práce
The efficiency of the designed setup shall be verified on a testing JavaCard applet with a known interface (e.g., OpenPGP applet) and 1-2 smartcards with an unknown interface.
The thesis will cover the following topics:
- Survey of existing research articles on black-box API discovery methods with a focus on the area of smartcards.
- Extension of APDUFuzzer project with AFL fuzzer combined with power trace analysis recorded by digital oscilloscope.
- Analysis of fuzzing performance to discover the expected apdu payload using an applet(s) with a known interface as ground truth (e.g., OpenPGP or SimpleAPDU).
- Application of fuzzing setup on 1-2 cards with an unknown interface with results interpretation.
- A suggestion of techniques to cluster the same or very similar fuzzing "hits" together and how to extract apdu payload structure based on the hits obtained.
- Suggestions for further optimization of the fuzzing setup.
Literature:
APDUFuzzer project: https://github.com/petrs/pyAPDUFuzzer
Smart Card Handbook, W. Rankl, W. Effing, ISBN-10: 0470743670, Wille, 2010
american fuzzy lop (AFL) http://lcamtuf.coredump.cx/afl/
Picoscope https://www.picotech.com/products/oscilloscope
23. 5. 2019 13:18, doc. RNDr. Petr Švenda, Ph.D., učo 4085
- Zadáno/změněno 18. 6. 2019 17:08, Helena Kryštofová
- Záznam založen 2. 5. 2019 09:33, Jana Zemanová, učo 9619
- Zveřejnit od 20. 5. 2019 09:51, Helena Kryštofová
- Práce převzata 20. 5. 2019 09:51, Helena Kryštofová
 angličtina
Práce na příbuzné téma
Seznam prací, které mají shodná klíčová slova.
-
Synthesizing grammar of smart card commands
Mgr. Ondřej Kuhejda -
Reverzní inženýrství JavaCard appletu prováděného na čipové kartě
Mgr. Martin Prpič, učo 256137 -
Fuzzing of the OpenSC Project
Mgr. Veronika Hanulíková, učo 492760 -
The use of a power analysis for influencing PIN verification on cryptographic smart card
Mgr. Lukáš Folkman, učo 140414 -
Forensic profiles of certified cryptographic smartcards
Mgr. Martin Podhora -
Analýza mechanismu RMI u čipových karet s platformou JavaCard
Mgr. Martin Kvočka, učo 173286 -
Využití čipových karet pro službu Remsig
Mgr. Erik Horváth -
Collaborative RSA keypair generation and use
Mgr. Lukáš Zaoral
Složky
Soubory
-
Přidání souboru
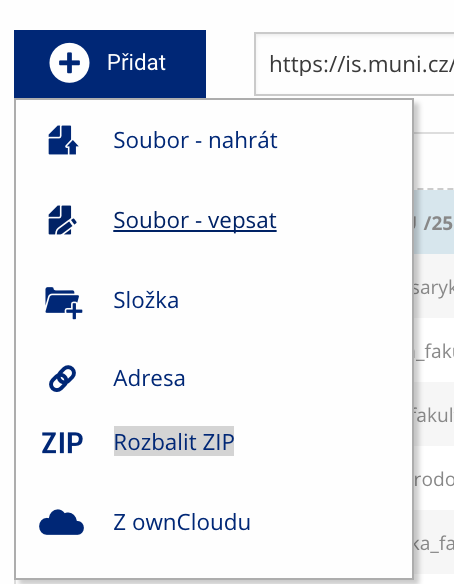 Soubor nebo složku lze nahrát pomocí tlačítka Přidat.
-
Další operace se soubory
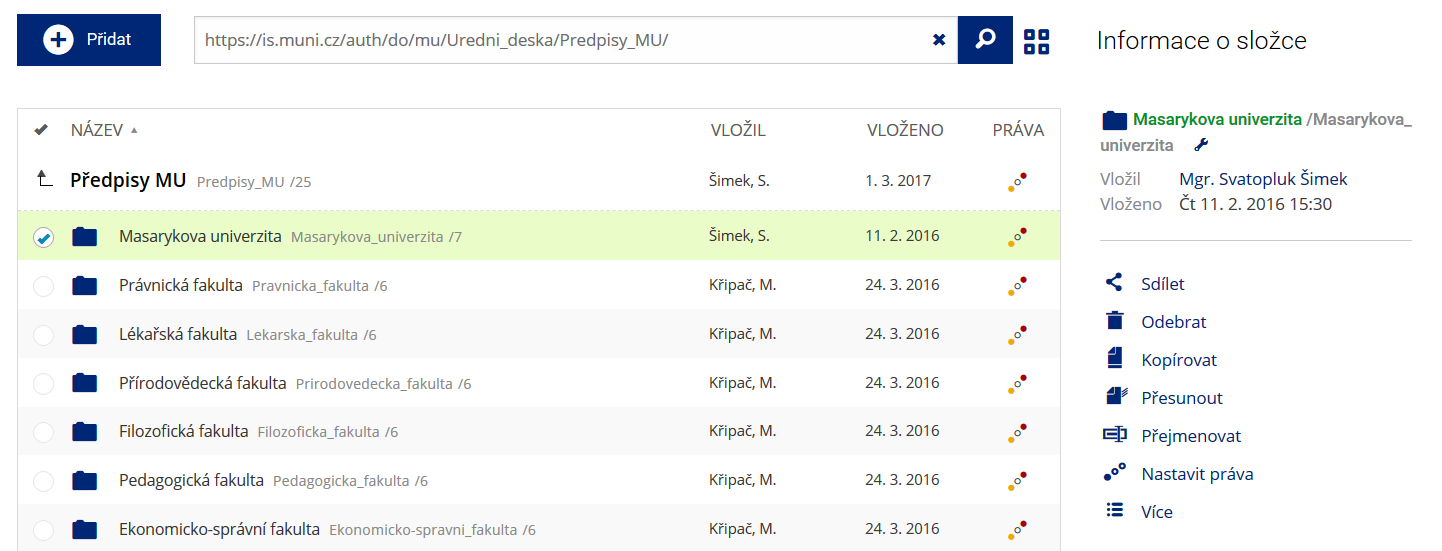 Podrobnosti lze zjistit označením příslušného řádku.
-
Pohled pro experty
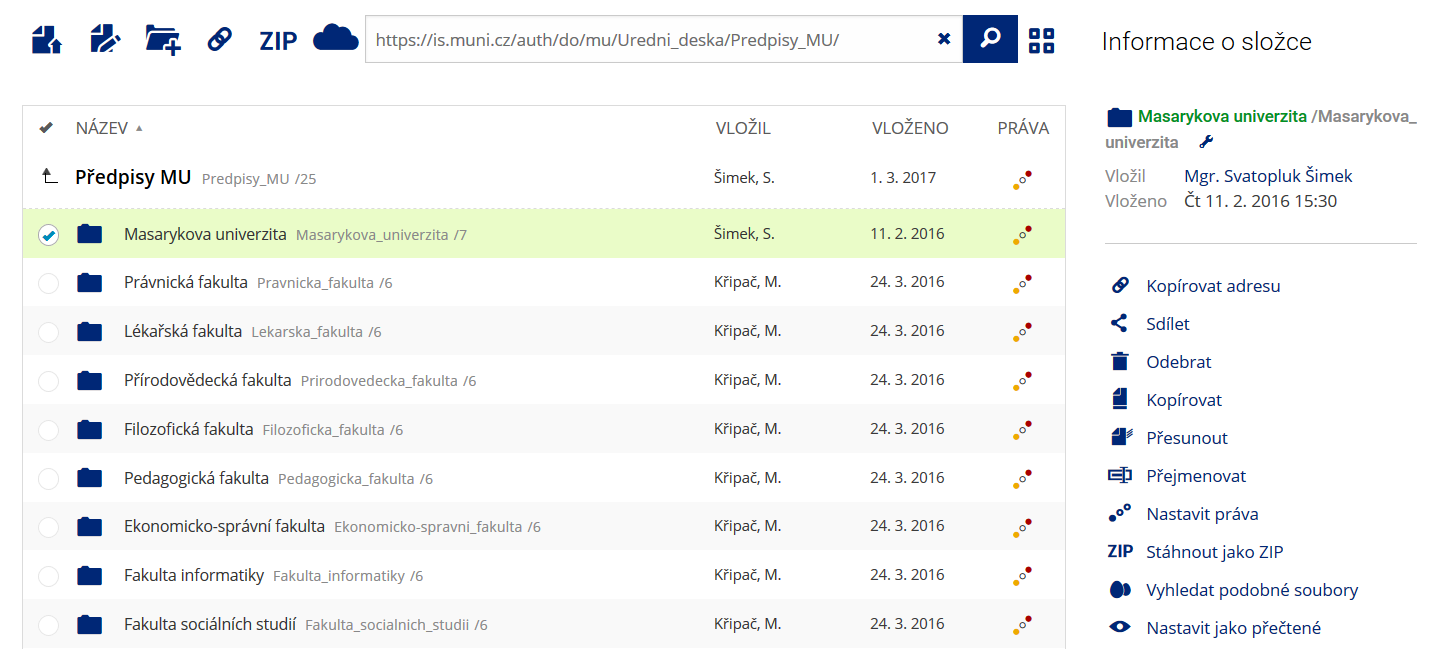 Pro častou práci je možné zvolit režim Více možností.
-
Vyhledávání souborů
 Vyhledávaný výraz můžete zadat přímo do adresního řádku.
-
Rychlý přístup k souborům
 Pomocí funkce Nedávné je možné se rychle vrátit k právě prohlíženým souborům. Oblíbené soubory je také možné označit Hvězdičkou.