Závěrečná práce: Adam Helc: Obtaining Information about Common Vulnerabilities and Exposures
Bakalářská práce
Obtaining Information about Common Vulnerabilities and Exposures
Anotace
Táto bakalárska práca predstavuje redizajn a implementáciu konektora CVE v rámci súboru nástrojov CRUSOE v reakcii na prechod Národnej databázy zraniteľností (NVD) z dátových zdrojov na REST API. Cieľom bolo zabezpečiť aktuálne získavanie a spracovanie údajov o zraniteľnostiach pre tímy kybernetickej bezpečnosti. Konektor integroval REST API NVD pre efektívne získavanie údajov, podporuje verziu 4 systému …více
Abstract
This bachelor’s thesis presents the redesign and implementation of the CVE connector within the CRUSOE toolset in response to the National Vulnerability Database (NVD) transition from data feeds to a REST API. The objective was to ensure up-to-date retrieval and processing of vulnerability data for cybersecurity teams. The connector integrated the NVD REST API for efficient data acquisition, supports …více
Zadání práce
The purpose of this thesis is to implement a new version of the CVE connector that is adapted to the mentioned changes. The thesis should fulfill the following tasks.
- Familiarize with the CVE connector, the NVD, and official documentation of the NVD's REST API.
- Update relevant parts of the CVE connector to use the REST API instead of downloading data feeds.
- Add support for the Common Vulnerability Scoring System (CVSS) of version 4. Update the classifier of vulnerabilities from [4] to use CVSS of version 4 because the NVD does not plan to use CVSS of version 2 in the future.
- Update parts of source code responsible for storing data to and interacting with the Neo4j database.
- Find a way to obtain information that an exploit and a patch exist for a vulnerability.
- Prepare how the CVE connector will be used in the docker environment and during orchestration in Temporal.
- Solve other tasks that will appear during the implementation.
[1] https://github.com/CSIRT-MU/CRUSOE/tree/main
[2] https://github.com/CSIRT-MU/CRUSOE/tree/main/crusoe_observe/cve-connector
[3] https://nvd.nist.gov/developers/vulnerabilities
[4] https://is.muni.cz/auth/publication/1407187/2018-NOMS-Community-Based-Platform-for-Vulnerability-Categorization-paper.pdf
23. 5. 2025 14:26, RNDr. Lukáš Sadlek, Ph.D., učo 445581
 angličtina
Práce na příbuzné téma
Seznam prací, které mají shodná klíčová slova.
-
Improving Cybersecurity Through Situational Awareness
RNDr. Martin Laštovička, Ph.D., učo 395855 -
Vulnerability management with Zabbix
Mgr. Adam Chovanec, učo 485311 -
Virtualization and repository management in academic environment
Mgr. Jakub Hadvig, učo 255815 -
Aplikace architektonických vzorů při vývoji mobilní aplikace pro Android
Mgr. Iveta Jurčíková -
Návrh IT služby pro zefektivnění procesu
Mgr. Tomáš Vestenický -
Aplikace pro hodnocení kyberbezpečnostního cvičení
Bc. Jan Laštůvka -
Komunitní portál pro repozitář datových sad síťového provozu
Mgr. Henrich Horváth -
Web Application for Laboratory Data Analysis and Visualization
Mgr. Šimon Mačejovský
Složky
Soubory
-
Přidání souboru
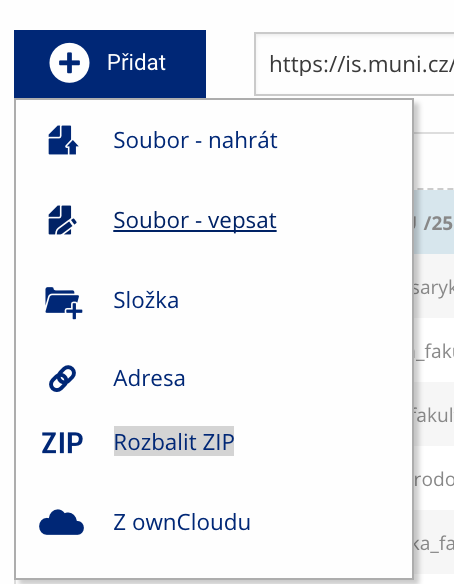 Soubor nebo složku lze nahrát pomocí tlačítka Přidat.
-
Další operace se soubory
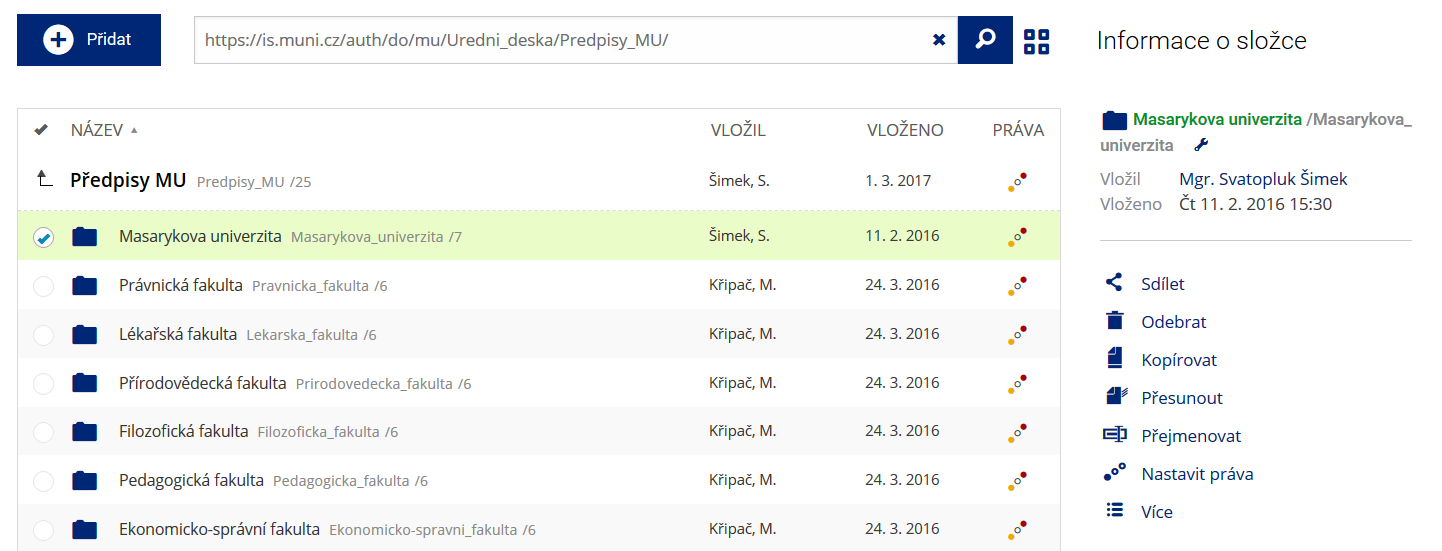 Podrobnosti lze zjistit označením příslušného řádku.
-
Pohled pro experty
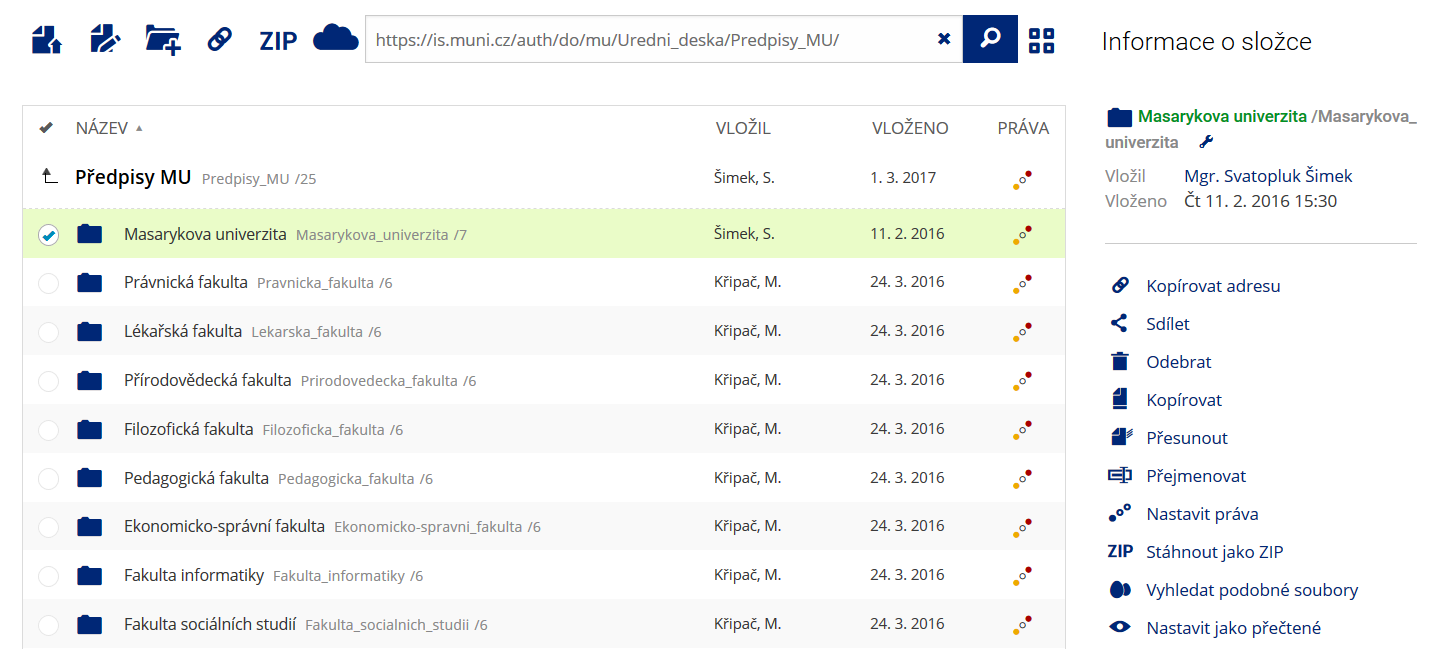 Pro častou práci je možné zvolit režim Více možností.
-
Vyhledávání souborů
 Vyhledávaný výraz můžete zadat přímo do adresního řádku.
-
Rychlý přístup k souborům
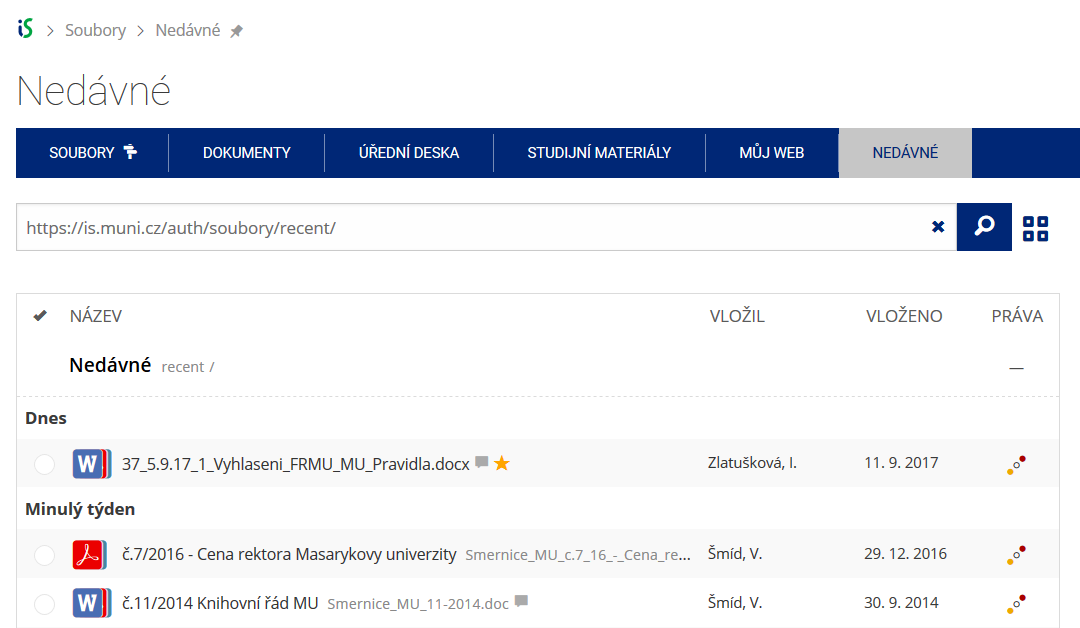 Pomocí funkce Nedávné je možné se rychle vrátit k právě prohlíženým souborům. Oblíbené soubory je také možné označit Hvězdičkou.