Závěrečná práce: Jiří Šimek: Processing of DNS BIND server logs for Cybersecurity Incident Response Teams
Bakalářská práce
Processing of DNS BIND server logs for Cybersecurity Incident Response Teams
Anotace
Cílem této práce je vytvořit nástroj pro analýzu logů DNS serveru pro potřeby Kyberbezpečnostního týmu Masarykovy univerzity. V rámci práce má být vytvořena konfigurace pro zpracování logů a jejich normalizaci za účely datové analýzy. Data pak budou předána architektuře Elastic stack, kterou budou zpracována a vizualizována v aplikaci Kibana. Výstupem práce je dashboard v aplikaci Kibana, jehož cílem …více
Abstract
The main goal of this thesis is to create a DNS server log analysis tool for the needs of the Cybersecurity Incident Response Team of Masaryk University. This goal will be achieved by implementing a pipeline, which receives raw logs produced by the server's logging service, extracts relevant information from the logs, and restructures them for the purpose of data analysis. The data is then shipped …více
Zadání práce
The output of the work will be the configuration of all tools used for log processing and dashboard in Kibana, containing visualizations of features of interest.
The work procedure will consist of the following steps:
- Learn how to log in BIND DNS, Syslog-ng, and ELK
- Description of DNS log features
- Log normalization
- Identification of features of interest that may occur in DNS queries in the MU network
- Design visualizations for identified features in Kibana
- Implement proposed visualizations within the Kibana dashboard
20. 12. 2021 10:23, RNDr. Stanislav Špaček, Ph.D., učo 324802
 angličtina
Práce na příbuzné téma
Seznam prací, které mají shodná klíčová slova.
-
Dashboard for visualizating security situation in computer network
Samuel Vadovič -
Dashboard for visualizating security situation in computer network
Samuel Vadovič -
Graph-based analytics and visualization of cybersecurity data
Ing. Martin Hesko -
Processing of the Data Measured by UAV
Mgr. Bedřich Said -
Vizualizace pro nástroj Flowmon DDoS Defender
Mgr. Ondrej Repa, učo 433704 -
Improving the ability to analyze and monitor logs from large-scale information systems
Mgr. Daniel Iľkovič -
Dashboard Visualizations in Ext.js
Ing. Dávid Želník, učo 469323 -
Dashboard pro operační centrum kyberbezpečnostního týmu
Mgr. Matej Šípka, učo 410043
Složky
Soubory
-
Přidání souboru
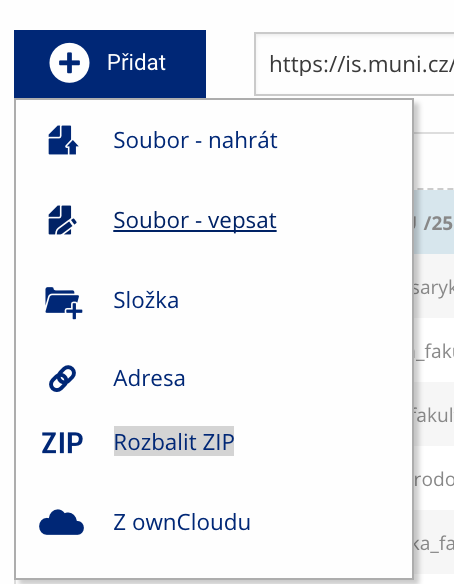 Soubor nebo složku lze nahrát pomocí tlačítka Přidat.
-
Další operace se soubory
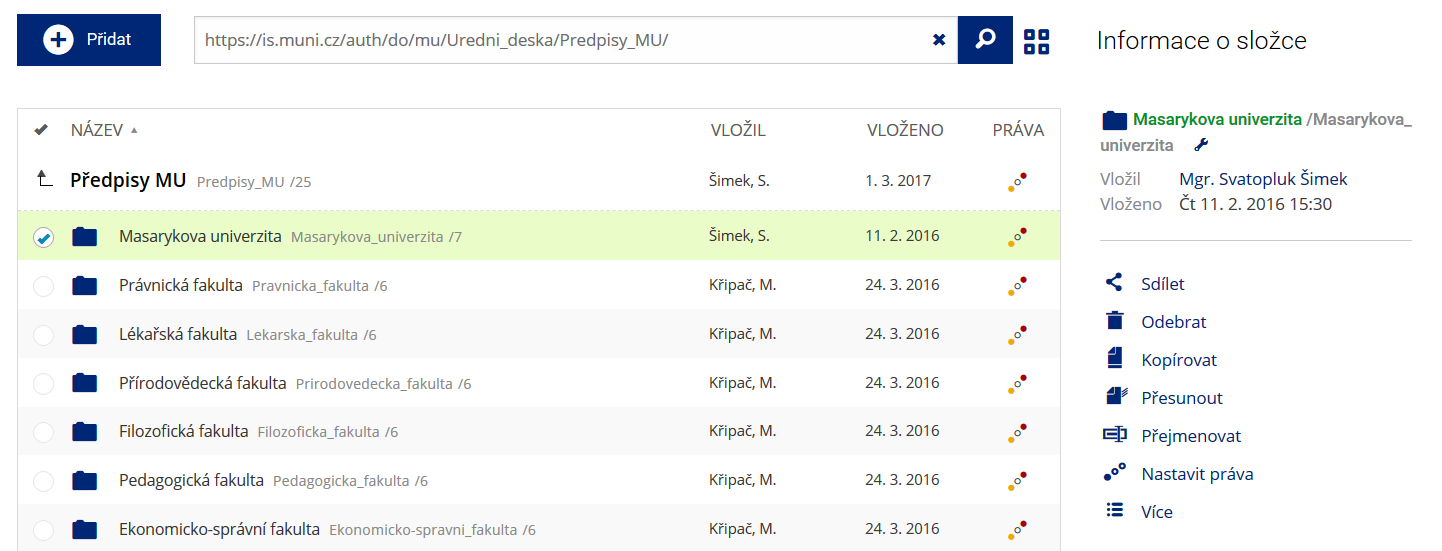 Podrobnosti lze zjistit označením příslušného řádku.
-
Pohled pro experty
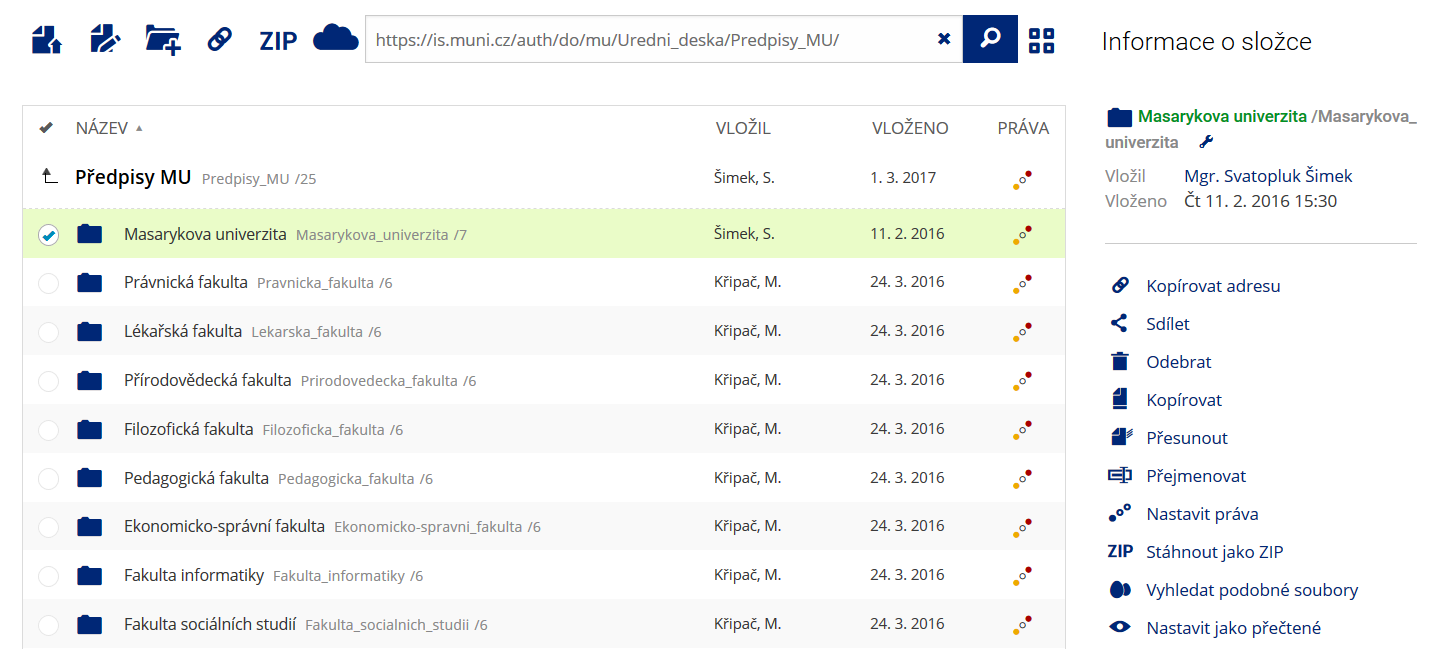 Pro častou práci je možné zvolit režim Více možností.
-
Vyhledávání souborů
 Vyhledávaný výraz můžete zadat přímo do adresního řádku.
-
Rychlý přístup k souborům
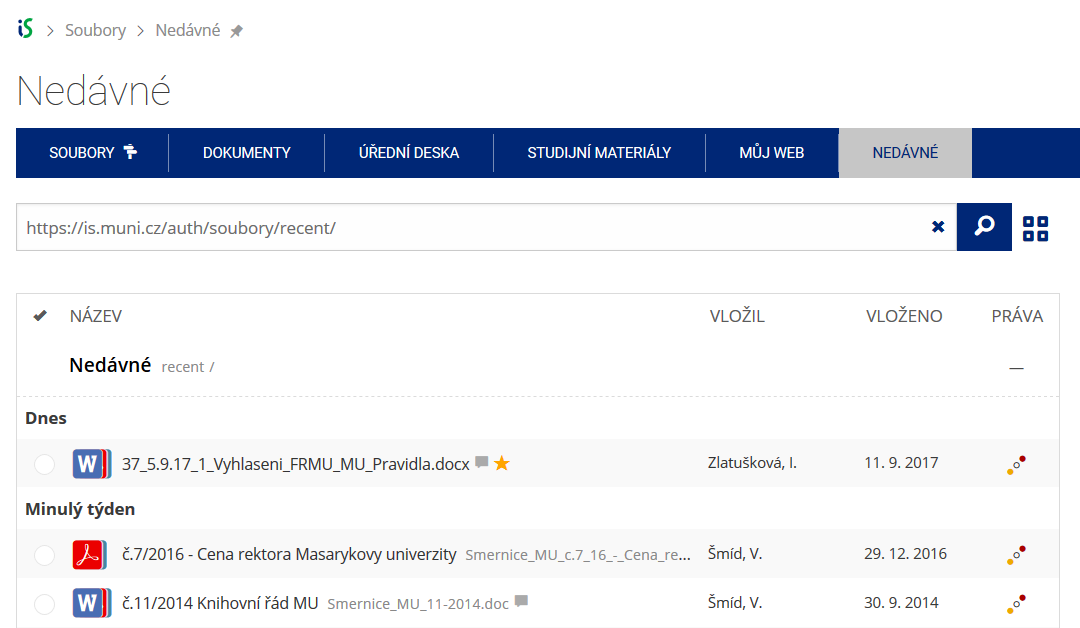 Pomocí funkce Nedávné je možné se rychle vrátit k právě prohlíženým souborům. Oblíbené soubory je také možné označit Hvězdičkou.