Thesis/Dissertation: Veronika Hanulíková, učo 492760: Fuzzing of the OpenSC Project
Bachelor's thesis
Fuzzing of the OpenSC Project
Abstract
Projekt OpenSC poskytuje middleware a nástroje pro používání čipových karet. Čipové karty jsou bezpečnostní hardware, který umožňuje bezpečně ukládat data a kryptografické klíče a dále s nimi provádět kryptografické operace. Je důležité zajistit, aby projekt OpenSC správně pracoval s daty přijatými od čipových karet. K tomuto účelu je možné využít fuzz testování neboli fuzzing. Fuzzing je vhodná metoda …more
Abstract
The OpenSC project provides middleware and tools for using smart cards. Smart cards are secure hardware that allows to securely store the data and cryptographic keys and perform cryptographic operations with it. It is important to ensure that OpenSC correctly handles data it receives from smart cards, and fuzzing can be used for this purpose. Fuzzing is a suitable method for testing and detecting errors …more
Thesis description
The OpenSC project [1] is an open-source middleware providing a set of libraries and utilities for the interaction with smartcards, mainly focusing on cryptographic smartcards and their applications. OpenSC processes potentially untrusted inputs from the hardware, and if the input is not handled correctly, it might pose a security threat.
A simple yet quite efficient method for discovering issues in input handling is fuzzing. Continuous fuzzing of open-source software is a longstanding effort of the OSS-Fuzz project [2]. The OSS-Fuzz project already supports OpenSC fuzzing, but the code coverage of existing fuzz targets is limited only to the most common drivers and operations.
The goal of this work is to analyze the current state of OpenSC fuzzing support in the OSS-Fuzz and suggest and implement improvements to the fuzz targets in the OpenSC project. For this purpose, the student will:
- Learn about fuzz testing techniques and the OSS-Fuzz environment.
- Study existing fuzz targets in the OpenSC project, and analyze their code coverage and limitations.
- Propose and implement at least three new fuzz targets in the OpenSC project and try to improve existing fuzz targets based on the acquired data from OSS-Fuzz.
- Evaluate testing results with the implemented enhancements.
- OpenSC: Open-source smart card tools and middleware
https://github.com/OpenSC/OpenSC - OSS-Fuzz: Continuous Fuzzing for Open Source Software
https://github.com/google/oss-fuzz
19/5/2022 17:47, RNDr. Antonín Dufka, Ph.D.
 English
Theses on a related topic
List of theses with an identical keyword.
-
Using fuzzing for Linux disk encryption tools
Mgr. Daniel Zaťovič, UČO 469348 -
APDUFuzzer: blackbox recovery of smartcard API
Mgr. Peter Benčík -
Extension of fuzzing for Linux disk encryption
Bc. David Flor, UČO 493294 -
Synthesizing grammar of smart card commands
Mgr. Ondřej Kuhejda -
File Fuzzing in development process
Mgr. Dávid Pribula -
Cryptographic policies for private key operations
Mgr. Martin Sečkár, UČO 540471 -
Motivation, evaluation preference and personality of adult learners and language teachers role- case study
Mgr. Andrea Danišová -
Ice-hockey players' efficiency testing
Bc. David Kazda
Folders
Files
-
Přidání souboru
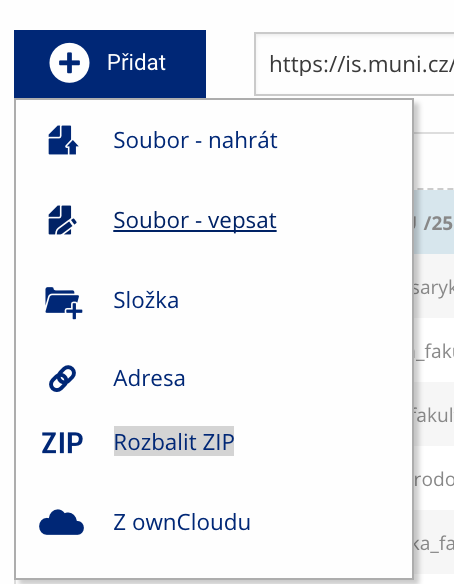 Soubor nebo složku lze nahrát pomocí tlačítka Přidat.
-
Další operace se soubory
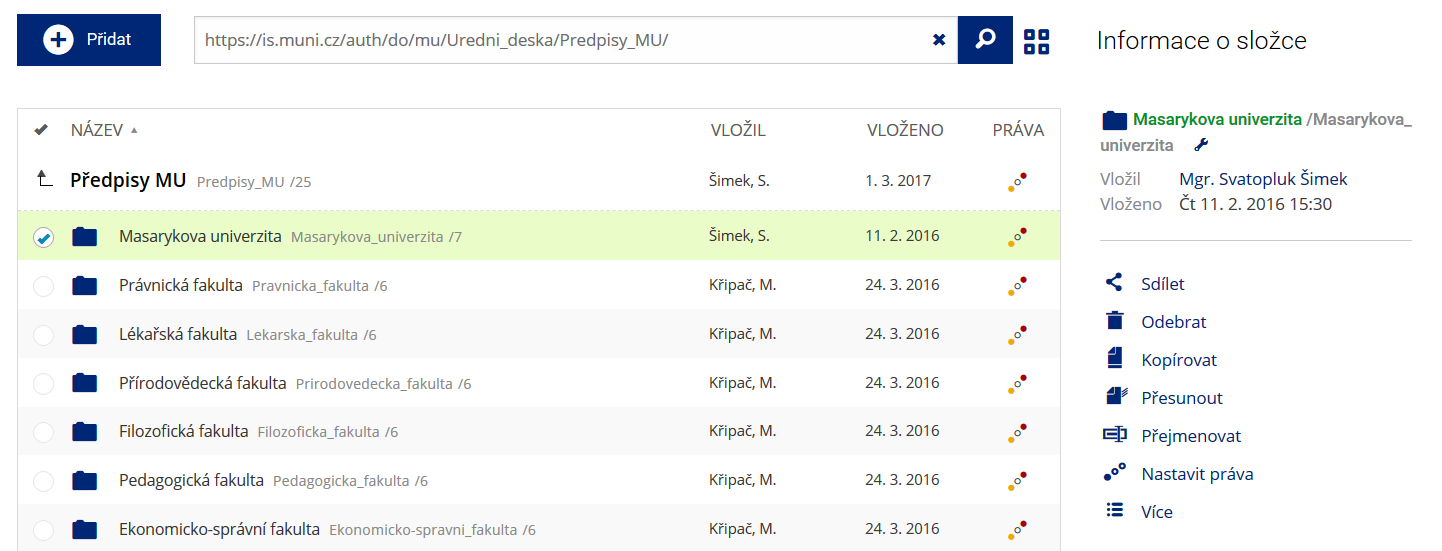 Podrobnosti lze zjistit označením příslušného řádku.
-
Pohled pro experty
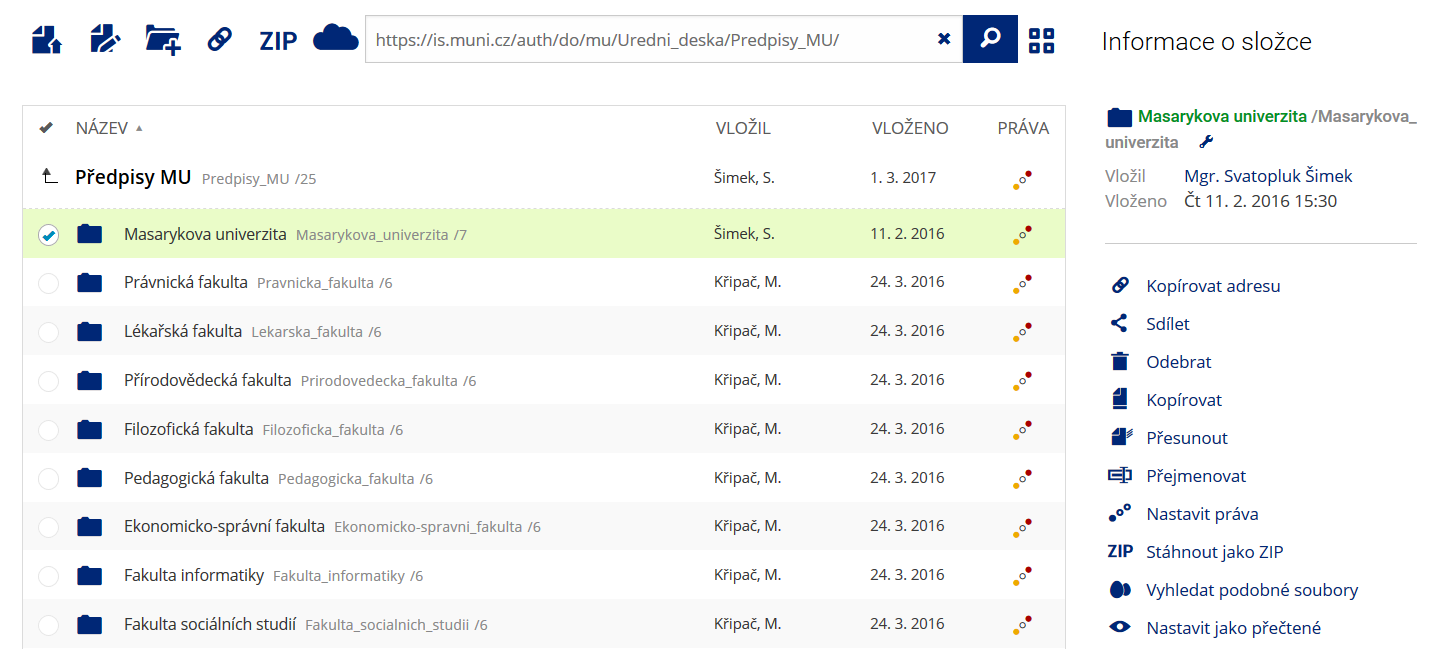 Pro častou práci je možné zvolit režim Více možností.
-
Vyhledávání souborů
 Vyhledávaný výraz můžete zadat přímo do adresního řádku.
-
Rychlý přístup k souborům
 Pomocí funkce Nedávné je možné se rychle vrátit k právě prohlíženým souborům. Oblíbené soubory je také možné označit Hvězdičkou.