Závěrečná práce: Bc. Michal Čaniga: Porovnanie nástrojov na vynútenie politík pre Kubernetes klastre v podnikovom prostredí
Diplomová práce
Porovnanie nástrojov na vynútenie politík pre Kubernetes klastre v podnikovom prostredí
Comparison of policy engines for enterprise scale Kubernetes clusters
Anotace
Monolitické aplikácie v praxi začínajú byť raritou. Nemožnosť škálovania špecifických častí, úzke previazanie častí systému spôsobujúce obtiažne zavedenie zmien v systéme, zložitá kolaborácia množstva tímov nad jedným zdrojovým kódom a ďalšie praktické problémy s ich vlastnosťami viedli k rozdeleniu systému na samostatné, menšie aplikácie, komunikujúce pomocou rozhraní, ktoré voláme mikroslužby. …více
Abstract
Monolithic applications are becoming a rarity in practice. The impossibility of scaling specific parts, the close connection of parts of the system are making it difficult to introduce changes in the system, the complex collaboration of a number of teams over one source code and other practical problems with their properties led to the division of the system into separate, smaller applications, communicating …více
Zadání práce
16. 12. 2023 16:10, RNDr. Marek Kumpošt, Ph.D., učo 44545
 slovenština
Konzultant
Práce na příbuzné téma
Seznam prací, které mají shodná klíčová slova.
-
Distributed Application Architecture Patterns
Mgr. Juraj Fiala -
A Platform for Benchmarking Microservices Performance Anomaly Detection
Ing. Dominik Kozubík -
Contract Testing in Heterogeneous Distributed Systems
Mgr. Dominik Labuda -
Integrating Apiman gateway with OpenShift
Mgr. Jakub Čecháček -
Integrating Apiman gateway with OpenShift
Mgr. Jakub Čecháček -
Automating Bug Bounty
Mgr. Ján Masarik -
Podpora clusteringu pro CDI komponenty na platformě SilverWare
Mgr. Slavomír Krupa, učo 396455 -
Adapting a Web Application to Run on a Secure Cloud Platform
Ing. Andrej Valíček
Složky
Soubory
-
Přidání souboru
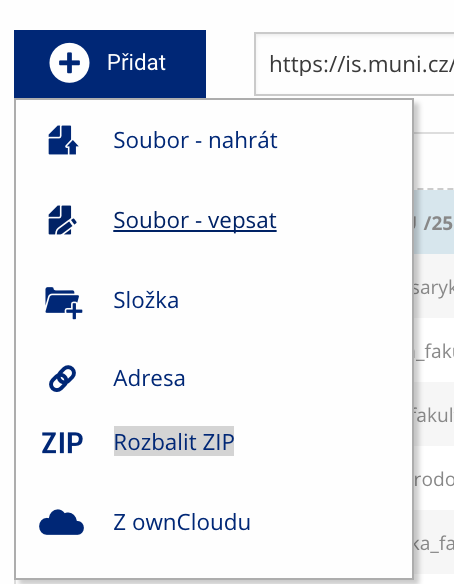 Soubor nebo složku lze nahrát pomocí tlačítka Přidat.
-
Další operace se soubory
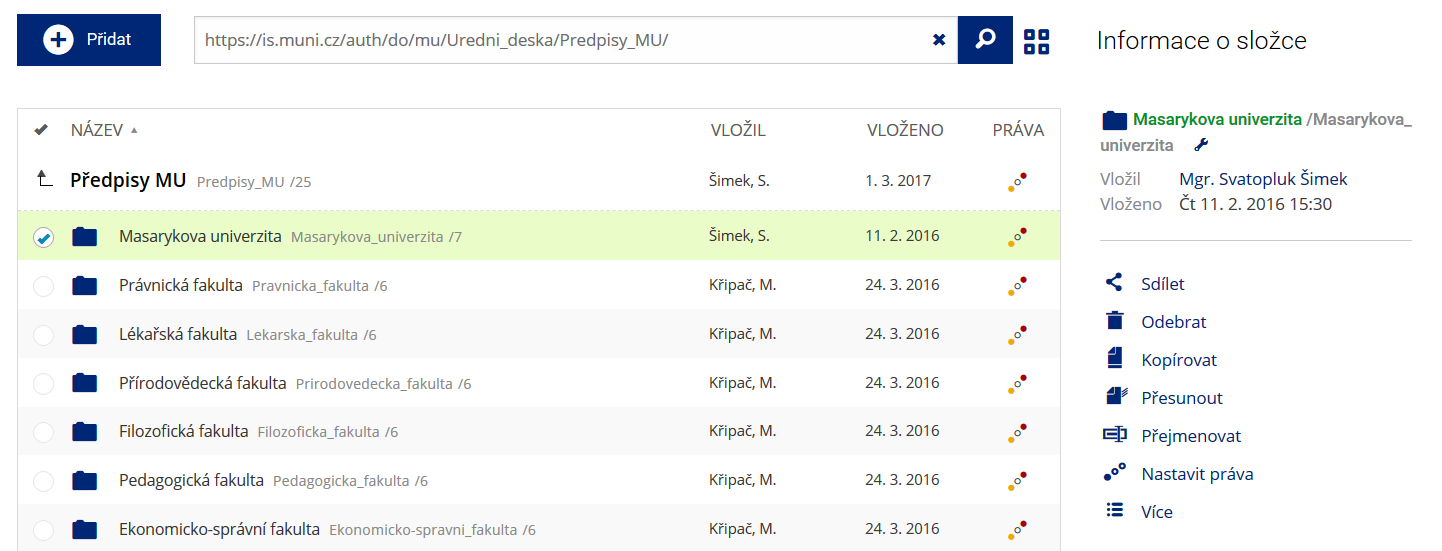 Podrobnosti lze zjistit označením příslušného řádku.
-
Pohled pro experty
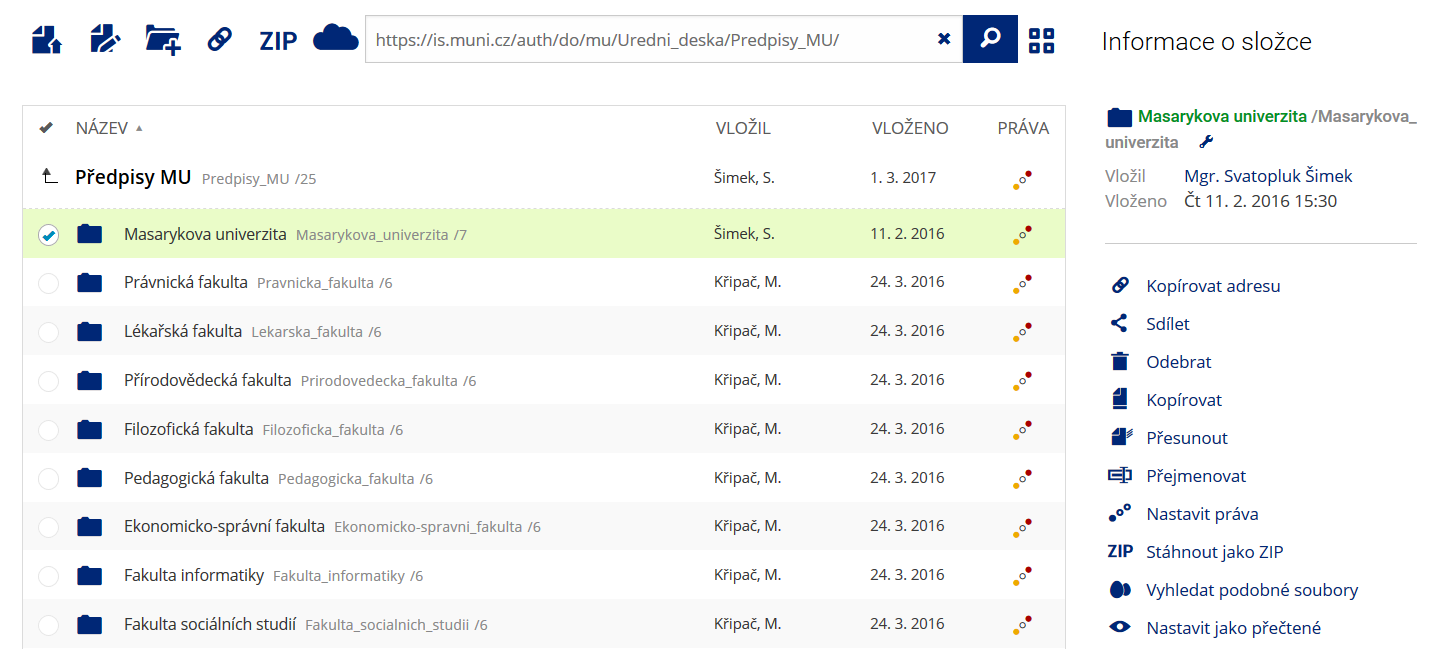 Pro častou práci je možné zvolit režim Více možností.
-
Vyhledávání souborů
 Vyhledávaný výraz můžete zadat přímo do adresního řádku.
-
Rychlý přístup k souborům
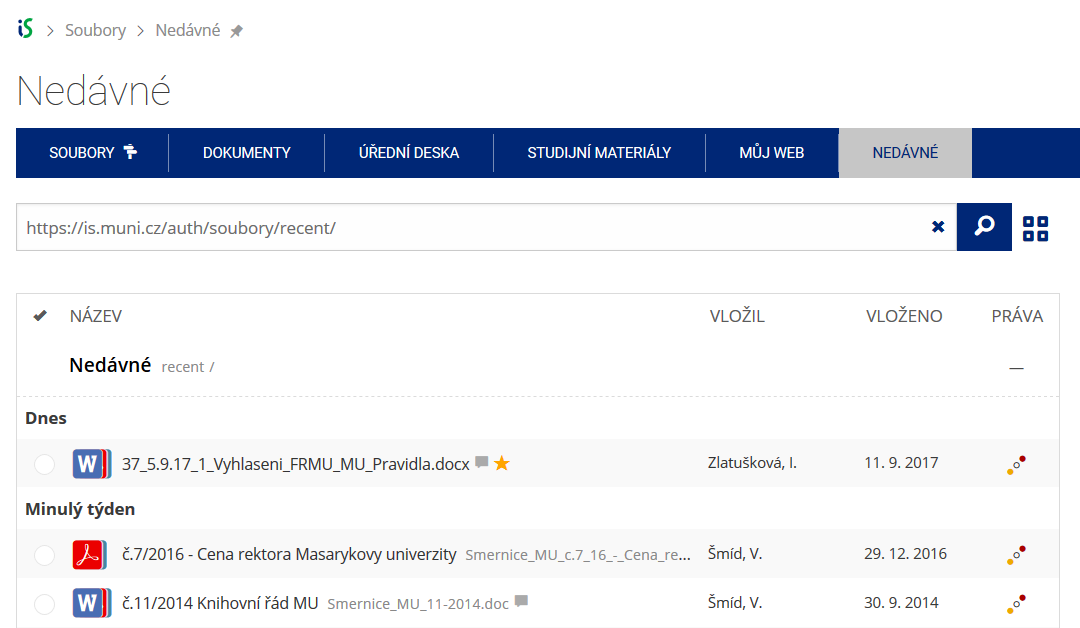 Pomocí funkce Nedávné je možné se rychle vrátit k právě prohlíženým souborům. Oblíbené soubory je také možné označit Hvězdičkou.